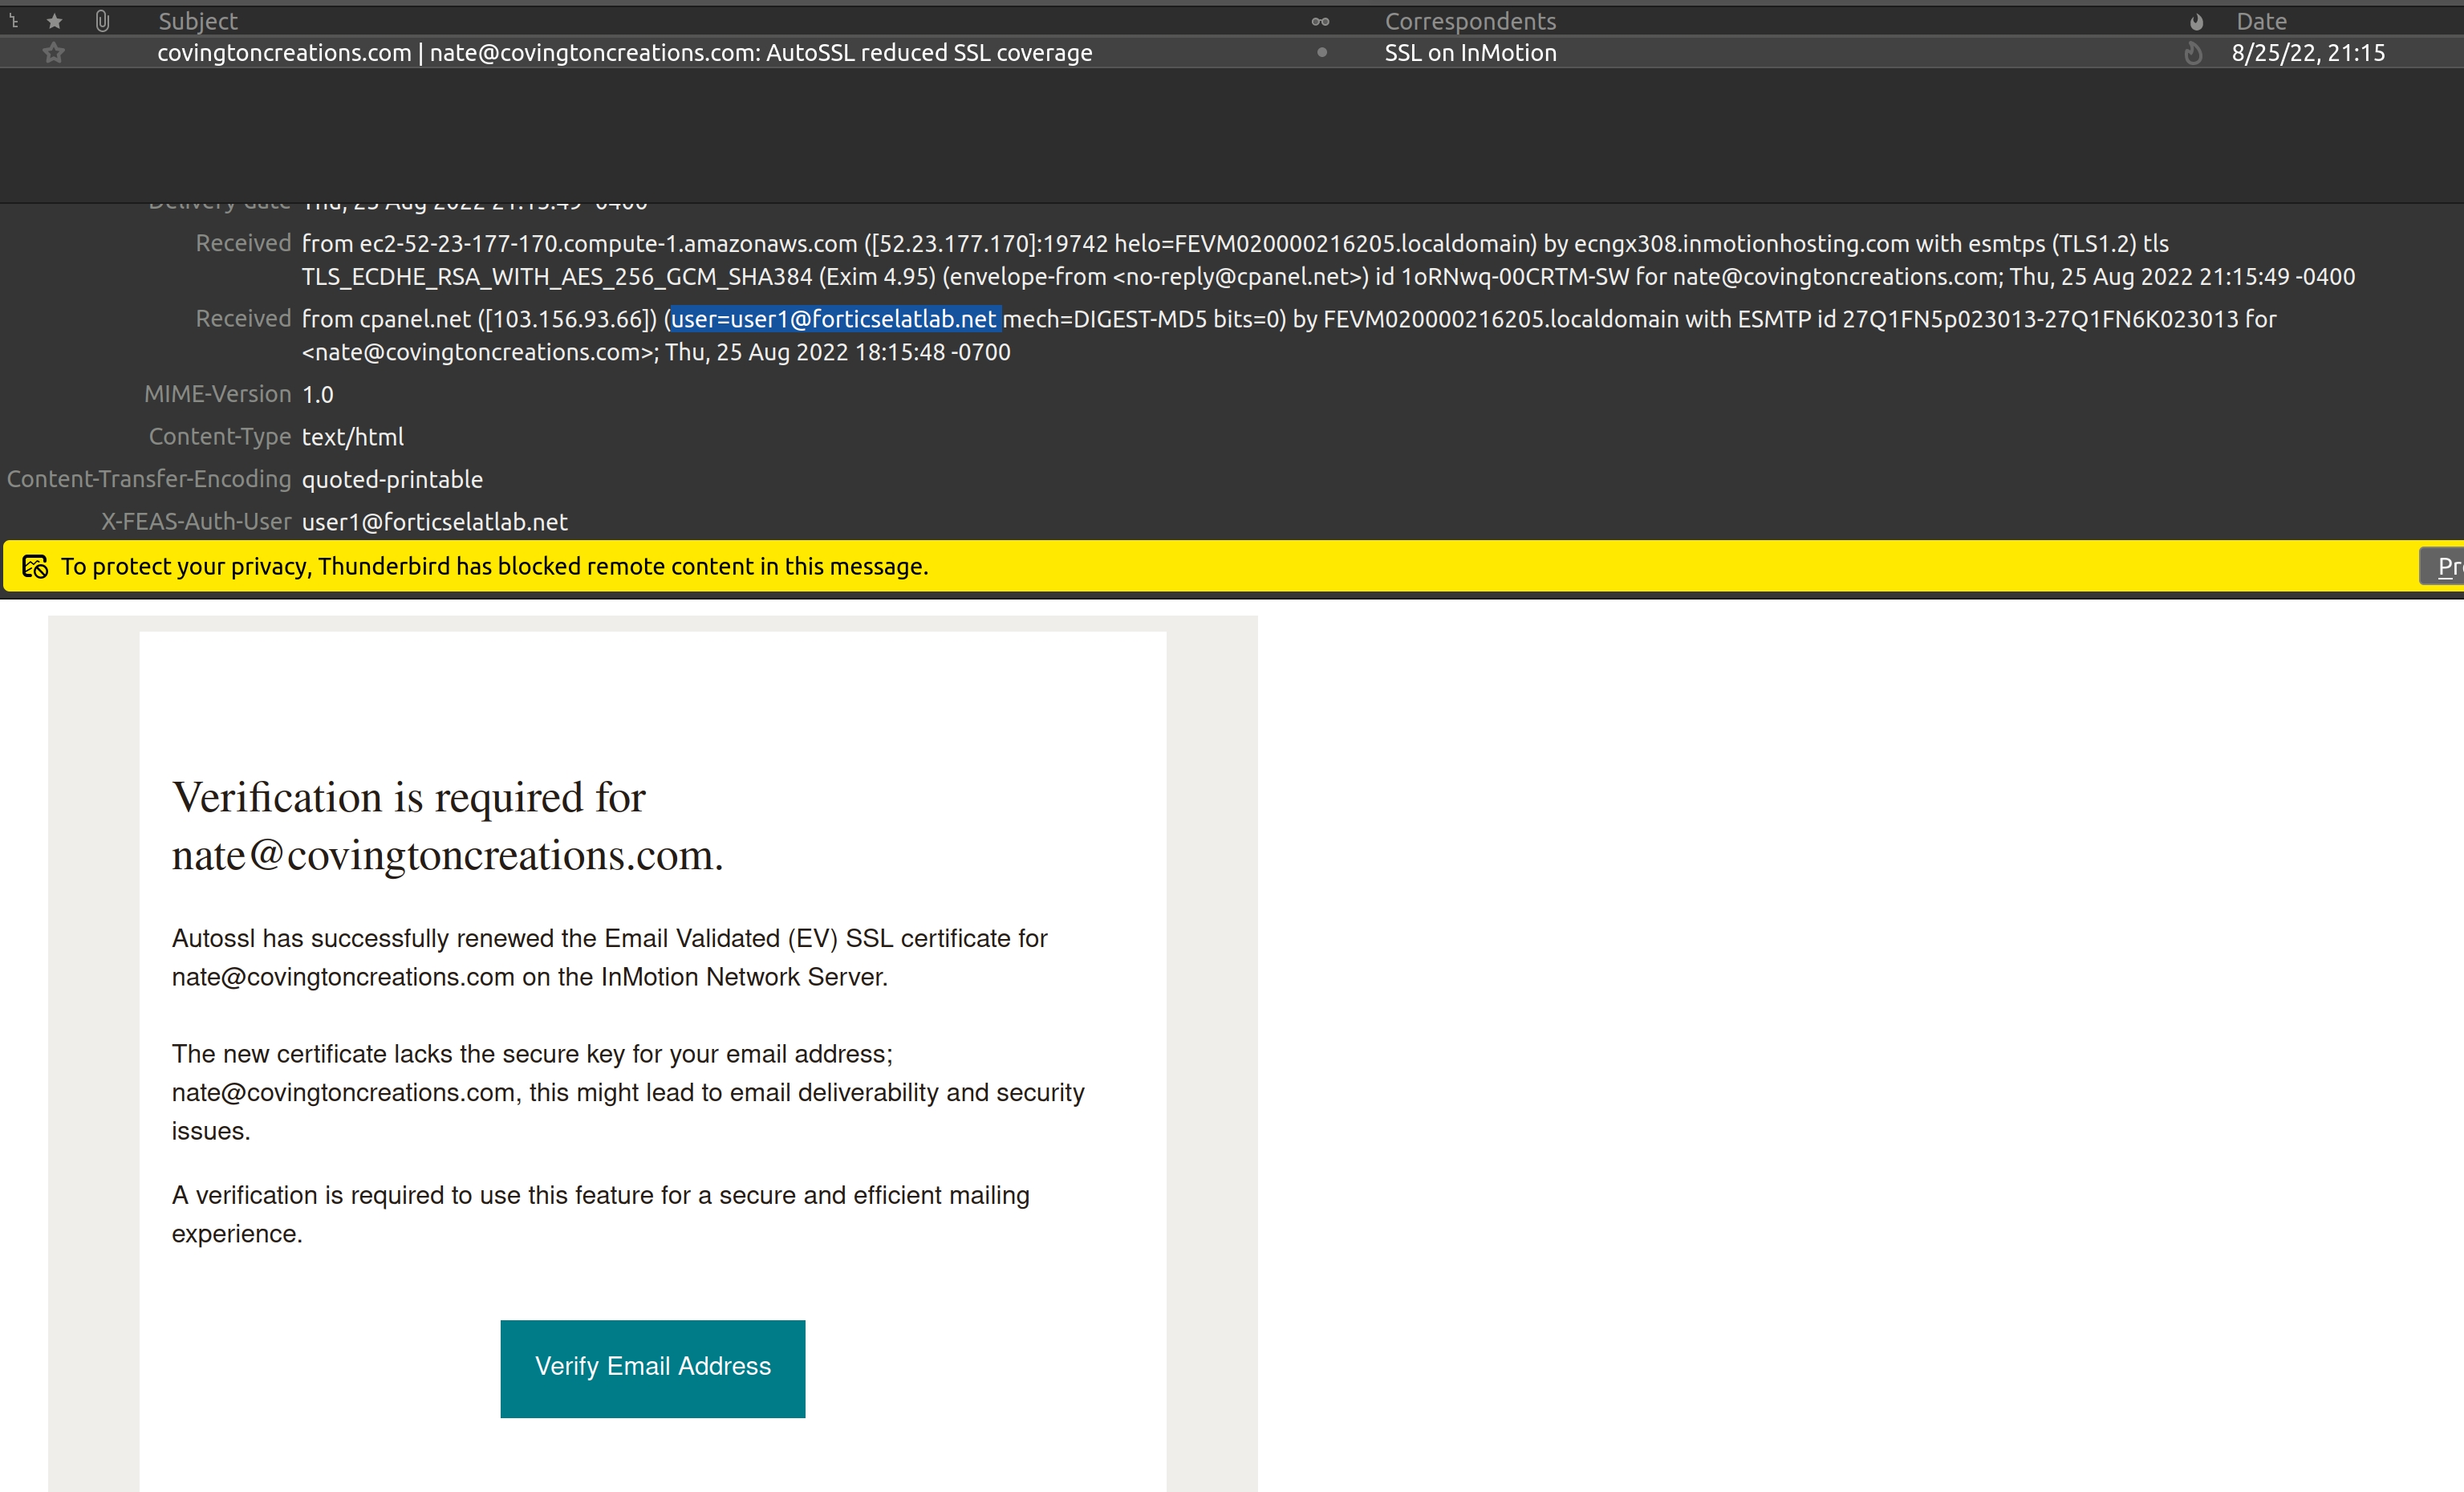
Beware! Fake emails being sent to InMotion customers - one of my other clients forwarded me the same thing last night - it looks like some bad actor has received a copy of InMotion's customer database. Do not click on the "Verify Email Address" link in these emails!
cpanel.net is a legitimate site but this emails are spoofed / fake!
From:
Subject:
example.com |
Message Content:
Verification is required for
Autossl has successfully renewed the Email Validated (EV) SSL certificate for
The new certificate lacks the secure key for your email address;
A verification is required to use this feature for a secure and efficient mailing experience.
Verify Email Address
© 2001-2022 InMotion®, All Rights Reserved.
Raw Message Headers, for forensic analysis:
from ec2-52-23-177-170.compute-1.amazonaws.com ([52.23.177.170]:19742 helo=FEVM020000216205.localdomain) by ecngx308.inmotionhosting.com with esmtps (TLS1.2) tls TLS_ECDHE_RSA_WITH_AES_256_GCM_SHA384 (Exim 4.95) (envelope-from <
from cpanel.net ([103.156.93.66]) (user=
How to check if your email was fake, too:
- Pull up the email in question using your mail program (Outlook, Thunderbird, Webmail, etc)
- Look for the option that displays the raw message headers. Normally this is in "View -> Headers -> All"
- Check to see if the email addresses match the sender in "From" - in my case the "mismatch" is
This email address is being protected from spambots. You need JavaScript enabled to view it.
Edit February 2, 2023:
I received another one like this from
SSL Certificate update for
InMotion SSL Verification.
We are updating our SSL Certificate for all emails on the InMotion Server.
You are required to confirm your email:
Please confirm your email address using the link below:
Confirm email
(linked to https:// jibberish.ipfs.dweb.link/#
If you have any questions, our support team is just a step away via live chat, phone, and email, Monday - Friday, 9 a.m. - 6 p.m. EST.
Thanks!
InMotion Team
Raw Message Headers:
from [59.16.217.6] (port=39618 helo=savemail.savezone.co.kr) by me.myserver.com with esmtps (TLS1.2) tls TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA384 (Exim 4.95) (envelope-from <
